If you’re searching for WordPress repair permissions, you’re likely dealing with a site that cannot upload media, install updates, or access certain files correctly.
You may need to quickly restore the correct WordPress file and folder permissions or determine whether permissions are actually causing the problem.
This guide will walk you through both. You’ll learn how to repair permissions safely and rule them out when the real issue lies elsewhere, so you can fix the problem without putting your site at risk.
Most WordPress folders should be 755, most files should be 644, and wp-config.php should be tighter if your host supports it. Use a backup plugin before recursive changes, because one wrong permission or ownership command can break uploads, admin access, or the front end.
The safest repair is simple: set the normal baseline, test the exact thing that failed, and stop loosening permissions if the error continues. At that point, the issue is usually ownership, hosting rules, server security, storage limits, or WordPress user roles.
Use these values as your starting point:
| WordPress path | Safe common value |
|---|---|
| Folders | 755 |
| Files | 644 |
| wp-config.php | 600, 640, 440, or 400, based on host support |
| .htaccess | Usually 644 |
| wp-content/uploads | Folders 755, files 644 |
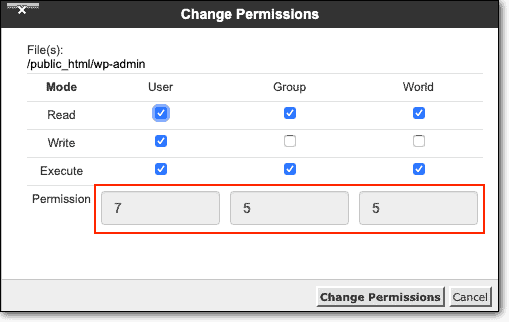
WordPress.org says file permissions vary by host. It also lists common shared-hosting values such as folders at 755 or 750, files at 644 or 640, and wp-config.php at 440 or 400 when the server can still read it. WordPress hardening guidance also gives recursive examples that set folders to 755 and files to 644.
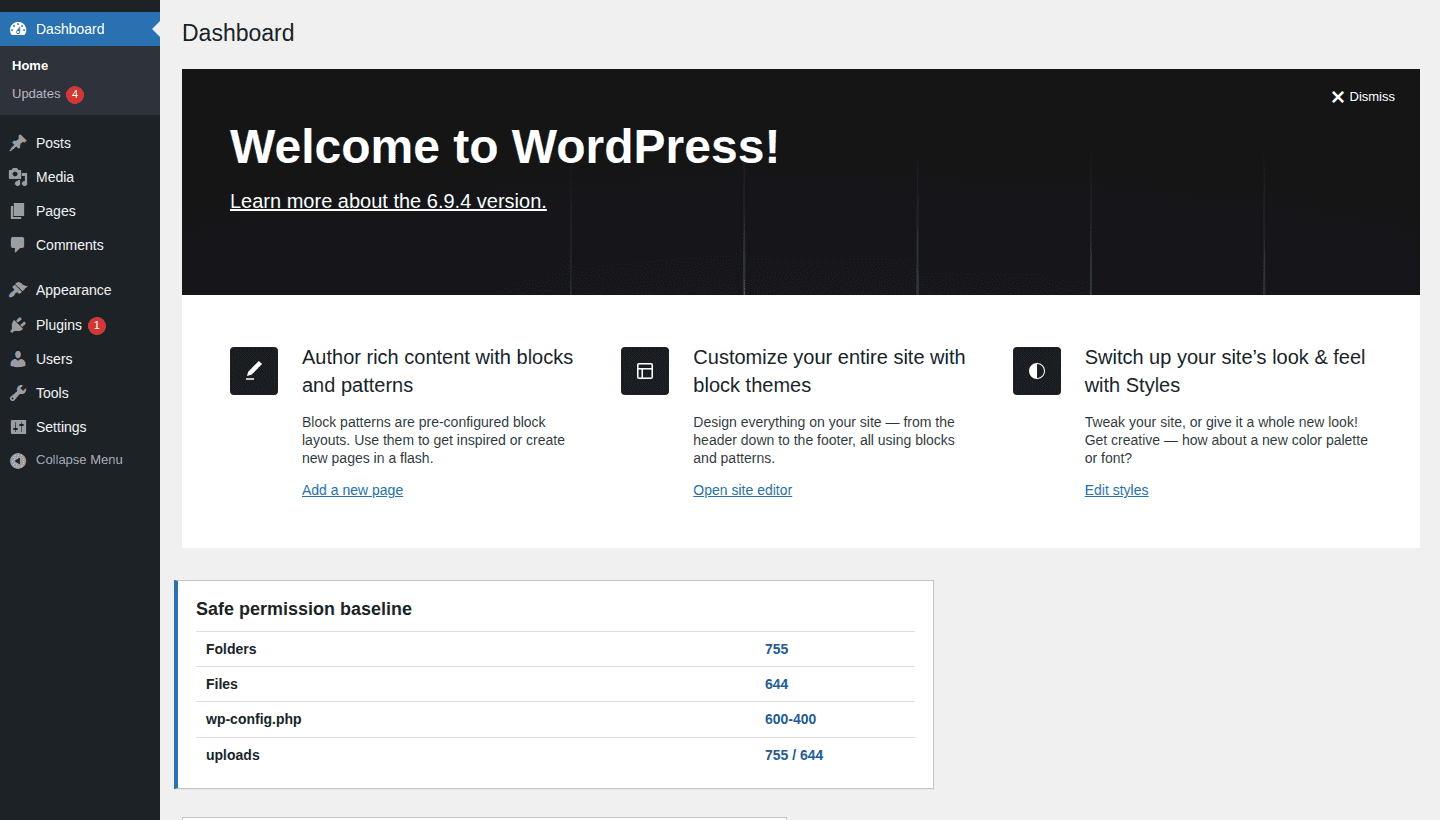
That means 755 and 644 are not magic numbers. They are the common baseline. A site can show those values and still fail if the wrong server user owns the files.
Match The Error To The Cause
Permission errors often appear during normal work. The message may say:
- Unable to create directory wp-content/uploads. Is its parent directory writable by the server?
- Installation failed: Could not create directory
- Permission denied
- No plugins are currently available
- Forbidden: You don’t have permission to access this resource
- Server unable to read htaccess file
Uploads need WordPress to write inside wp-content/uploads. Plugin and theme updates need write access inside wp-content, wp-content/upgrade, and the plugin or theme folder. Permalink changes may need WordPress to update .htaccess on Apache servers. A WordPress 403 Forbidden error can come from file permissions, but it can also come from server rules, security plugins, or blocked IPs.
Do not set everything to 777 just because one task failed. That can turn a small write problem into a security issue.
Prepare Before Changing Files
Before you repair permissions, do these checks:
- Find the real WordPress folder: Common roots include public_html, www, /var/www/html, /bitnami/wordpress, or a host-specific app folder.
- Record the current values: Save the current permission, owner, and group for the broken file or folder.
- Backup the site first: A recursive change affects many files at once. BlogVault is useful here because it gives you a backup, restore path, and staging option before you touch the filesystem.
- Use staging for busy sites: Test on staging first if the site handles sales, forms, courses, or memberships.
- Pick the least risky method: Use your host’s tool if it exists. Use SFTP if you do not have SSH. Use SSH only when you can confirm the path.
The WordPress export screen is a useful reminder to preserve site data before file work, but use a full backup and restore path for production repairs.
Choose Your Repair Method
Use the route that matches your access:
| Your situation | Best first option |
|---|---|
| Managed WordPress hosting | Host reset tool or host support |
| cPanel, Plesk, or similar panel | File Manager or WordPress Toolkit |
| No SSH access | SFTP or FTPS |
| Comfortable with terminal commands | SSH |
| Dashboard works, but you are not technical | Permission repair plugin |
| Values keep reverting | Host support |
Managed hosts often control ownership and server rules. Their reset tool is safer than a copied command because the host knows the correct account user and server setup.
Cloud platforms can also behave differently. Azure App Service and similar platforms may control or virtualize file modes. Bitnami and Lightsail WordPress images may use owners such as bitnami:daemon, so a generic www-data command can be wrong.
A) SFTP Or FTPS
Use SFTP or FTPS instead of plain FTP because your login is encrypted while it travels over the network. This method is best when you do not have SSH.
- Connect to the server securely: Open your SFTP or FTPS client and connect with the FTP credentials from your host.
- Open the WordPress root folder: Confirm you can see wp-admin, wp-content, and wp-includes.
- Show hidden files: Make sure .htaccess is visible if your site uses Apache.
- Set folders separately: Apply 755 to folders only.
- Set files separately: Apply 644 to files only.
- Tighten wp-config.php carefully: Try the tighter value your host supports, such as 600, 640, 440, or 400.
- Retest the failed action: Upload the image, update the plugin, or save the setting that failed.
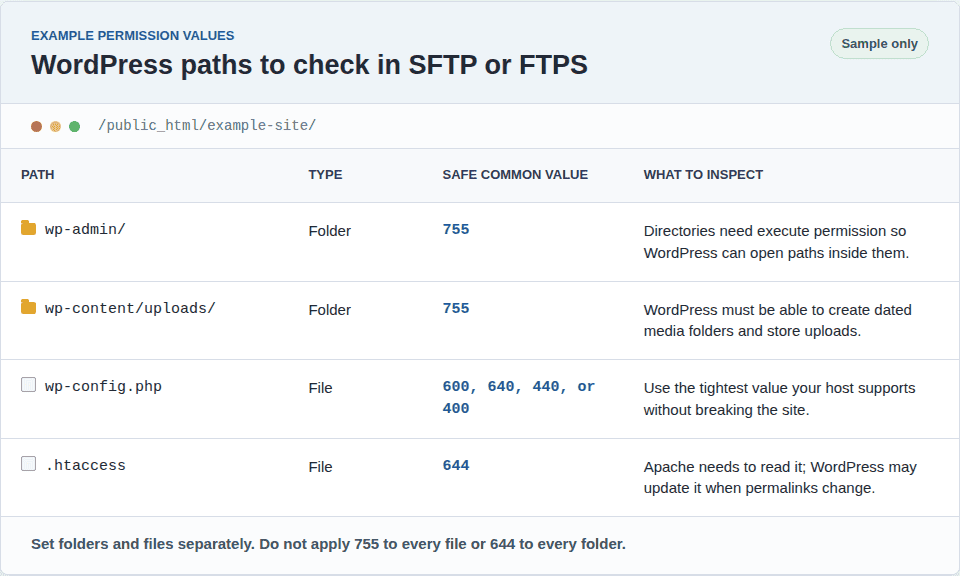
Do not apply 755 to every file. Do not apply 644 to every folder. Files and folders need different access rules. This example panel shows the kind of file and folder values to check in a secure file-transfer client.
B) SSH
Use SSH only if you can confirm the exact WordPress path. The examples below use a placeholder path. Replace it with your real WordPress root. First inspect the folder:
cd /path/to/wordpress
pwd
ls -la
Repair folders:
find /path/to/wordpress -type d -exec chmod 755 {} \;Repair files:
find /path/to/wordpress -type f -exec chmod 644 {} \;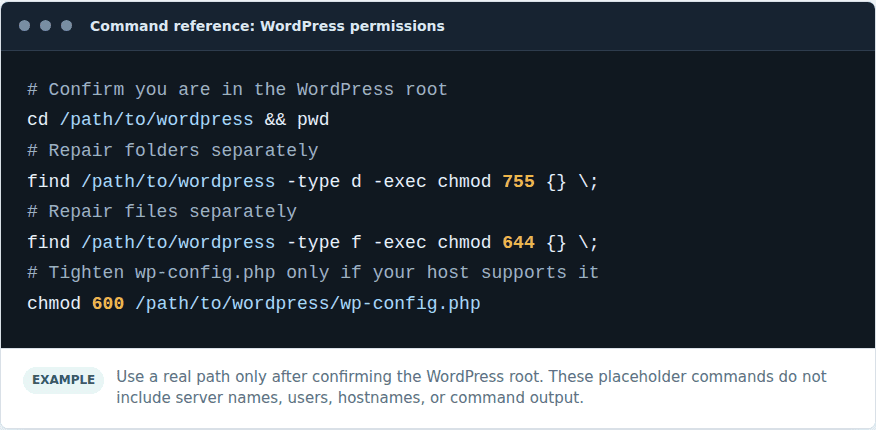
Then tighten wp-config.php only as far as your host allows:
chmod 600 /path/to/wordpress/wp-config.phpIf 600 breaks the site, use the previous working value or ask the host which value fits their setup. Some hosts need 640, 440, or 400 instead.
An ownership command may look like this:
chown -R accountuser:accountgroup /path/to/wordpressThat command is only safe after you know the right account user and group. On shared hosting, files are often best owned by your account user. On other setups, the web-server group may need read or write access.
C) Hosting Control Panel
If your host offers cPanel, Plesk, WordPress Toolkit, or a managed WordPress dashboard, check there before running terminal commands. Use the host tool when:
- permissions keep changing back;
- the owner name looks unfamiliar;
- the site was recently migrated;
- chmod changes do not work;
- the error mentions a host-controlled path;
- your site is on managed WordPress hosting.
A control panel may reset permissions with the correct owner and group. That matters because 644 can still fail when the wrong user owns the file.
If the tool does not fix the issue, contact support with the exact error, path, permission value, owner, group, and the action that caused the error. Ask them to check ownership and the PHP user, which is the server process that runs WordPress.
D) WordPress Repair Permissions Plugin
A WordPress permission repair plugin can help if you can still log in to WordPress and the server allows WordPress to change the affected files. Use this option when:
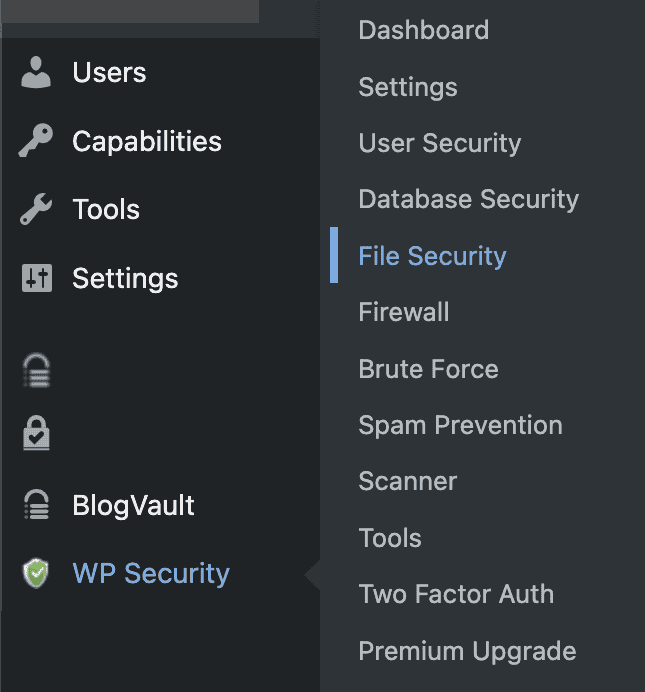
- you do not have SSH;
- the dashboard works normally;
- the problem affects common WordPress folders;
- you want a guided reset instead of manual changes.
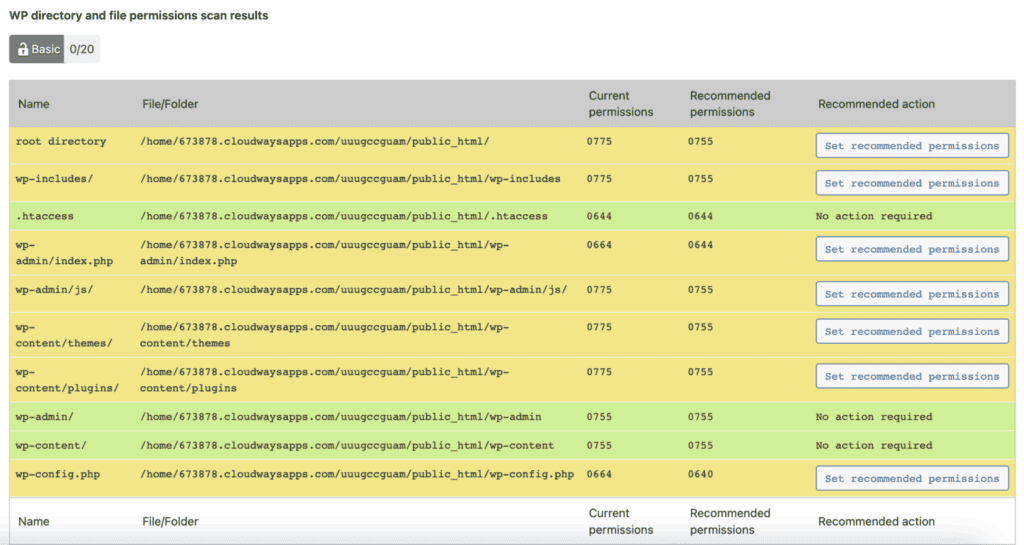
A plugin cannot overrule the server. If the owner is wrong, the host blocks file changes, SELinux denies writes, or cloud storage controls the path, the plugin can fail for the same reason WordPress failed.
Treat a plugin as a convenience tool, not a final diagnosis.
Handling Sensitive Paths Carefully
Some files and folders need extra care because they affect login, security, uploads, and page routing.
wp-config.php
wp-config.php stores database credentials and security salts. It should be more restricted than normal files.
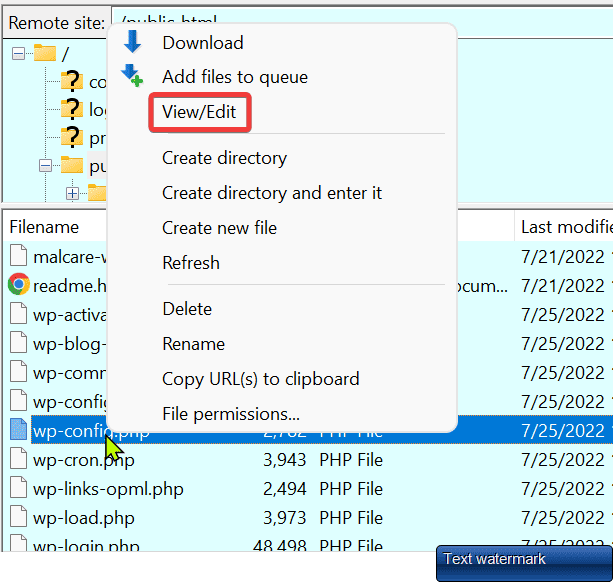
Common values include 600, 640, 440, and 400. Use the tightest value that still lets WordPress load. Never set it to 777, 666, or any value that makes it writable by everyone.
.htaccess
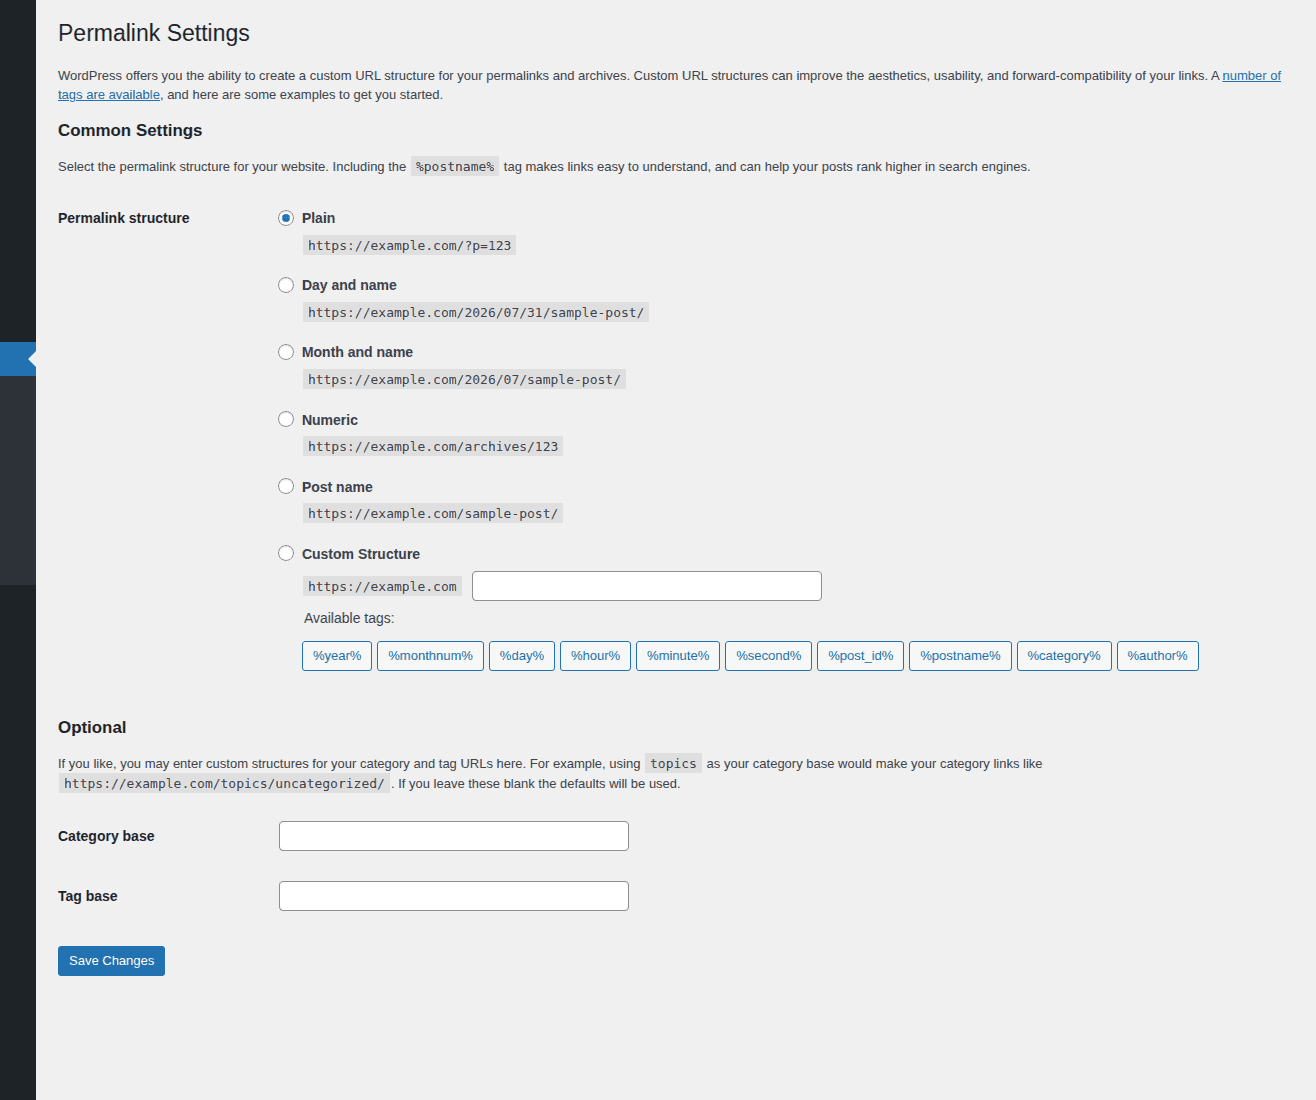
On Apache servers, .htaccess controls redirects, permalinks, and directory rules. It is usually 644. WordPress may need to write to it when you save permalinks.
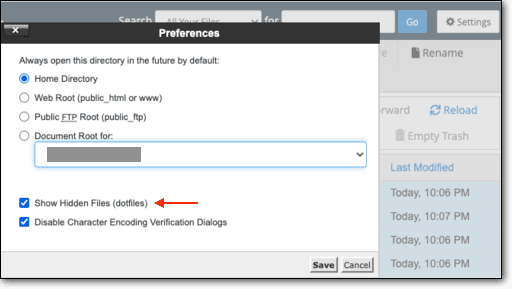
If the server cannot read .htaccess, you may see a 403 error. If the 403 remains after permissions look right, check redirect rules, security plugins, IP blocks, and host configuration.
wp-content/uploads
wp-content/uploads must be writable so WordPress can create media folders and store files.
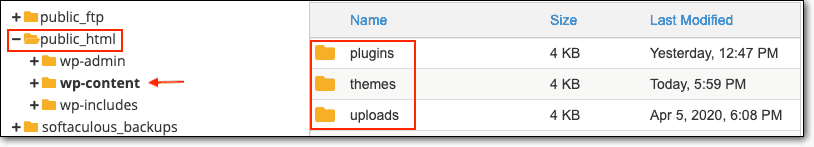
Start with folders at 755 and files at 644. If uploads still fail, check ownership, disk quota, the upload path setting, and host storage rules behind the WordPress failed to write file to disk error.
Plugins, themes, cache, and upgrade folders
Plugin updates can fail when WordPress cannot write inside wp-content. Theme installs, cache plugins, and core updates may fail for the same reason. Failed installs often mention wp-content/upgrade, a plugin folder, or a theme folder.
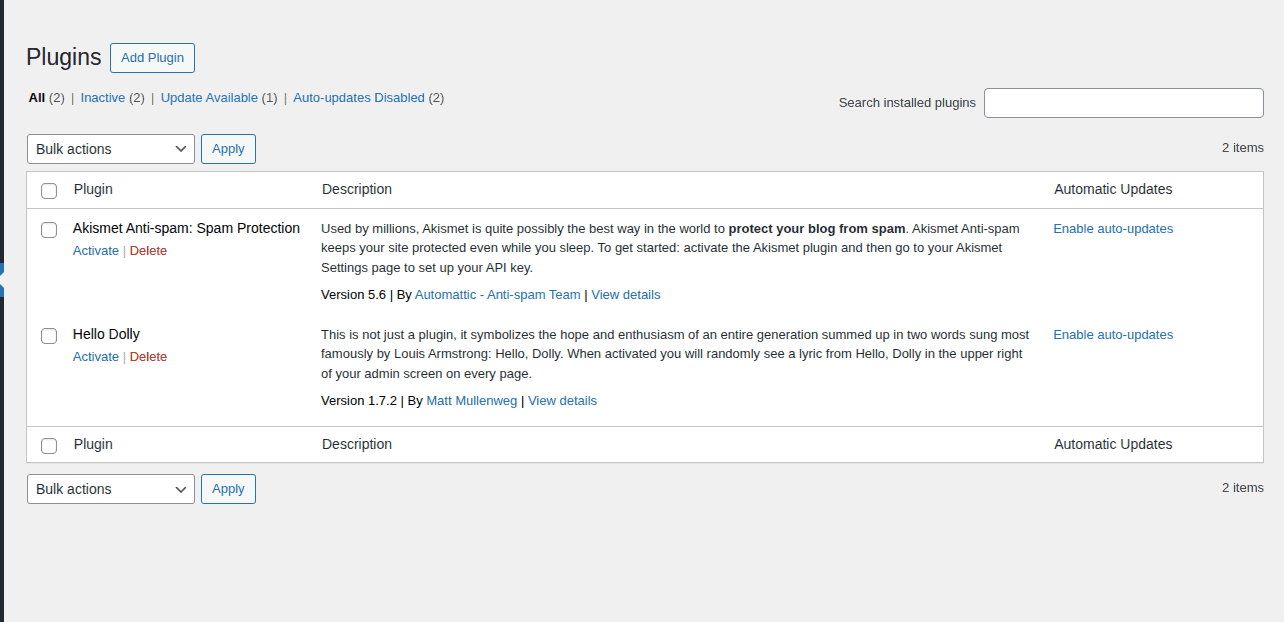
Repair the baseline first. If one plugin folder keeps failing, inspect that path by itself. Manual uploads and migrations often leave one folder with a different owner than the rest of the site.
If 755 And 644 Do Not Work
Do not keep making permissions looser. Look for the real blocker:
- wrong owner or group;
- PHP runs as a different user from the file owner;
- the host expects 750/640 or 775/664;
- SELinux blocks the write even though the visible permissions look correct;
- a managed host controls the filesystem;
- a cloud platform handles file modes differently;
- the disk is full or the account quota is reached;
- the upload path is wrong;
- a security plugin or server rule blocks the request;
- the error is about WordPress user roles, not file permissions.
Group-writable values such as 775 for folders and 664 for files can be correct when a trusted group needs write access. They should come from your host or server admin, not from guesswork.
Never Leave WordPress At 777
777 gives read, write, and execute access to the owner, the group, and everyone else. It may make an error disappear because almost any process can write. That is why it is dangerous.
WordPress.org warns against world-writable directories on shared or suexec-style hosting. A compromised account, script, or process can abuse loose permissions to change files that should be protected.
File Permissions vs User Roles
WordPress file permissions are server rules. WordPress user roles are dashboard rules.
The message You do not have sufficient permissions to access this page is often not a file permission problem. It can come from a changed admin role, broken capabilities, a plugin conflict, a failed update, database issues, or multisite super admin access.
If uploads and updates work but one admin page is blocked, check the user account and plugins before changing file modes.
Verify The Fix
After the repair, test the exact action that failed. Then check nearby behavior:
- Test uploads: Upload a small image.
- Test updates carefully: Update a low-risk plugin only if it is safe.
- Test permalinks: Save permalinks if .htaccess was involved.
- Test site access: Visit the homepage, an inner page, and the admin area.
- Check the original error: Confirm the exact message is gone.
- Review logs: Read WordPress or server error logs if your host exposes them.
- Watch for reversions: Check whether values change back after a few minutes.
If the fix works, remove any temporary broad permissions. If it fails, gather the exact error text, path, current permission, owner, group, hosting type, and recent changes before contacting support.
Prevent The Same Problem
Permission problems often start after migrations, restores, manual uploads, plugin installers, or server changes. Prevention is mostly about keeping file ownership and access consistent. Use these habits:
- Use secure transfers: Prefer SFTP or FTPS over plain FTP.
- Avoid live edits: Use staging when the site matters to revenue or leads.
- Back up before file work: Keep a restore point before updates, migrations, and permission changes.
- Track manual changes: Do not mix SFTP uploads, control-panel edits, and SSH ownership changes without noting what changed.
- Avoid world-writable paths: Do not leave files or folders open to everyone.
- Disable dashboard file editing when unused: This reduces the chance of risky theme or plugin edits from wp-admin.
- Ask after migrations: Have the host confirm the right owner and group if errors begin after a move.
FAQs
What are the correct WordPress file permissions?
For most sites, folders should be 755 and files should be 644. wp-config.php should usually be tighter, such as 600, 640, 440, or 400, depending on the host.
How do I fix the WordPress upload permission error?
Set wp-content/uploads folders to 755 and files to 644. If WordPress still cannot create the folder, check ownership, disk quota, upload path settings, and host storage rules.
Can I fix WordPress permissions without SSH?
Yes. Use SFTP, FTPS, your host’s File Manager, WordPress Toolkit, or a permission repair plugin if the dashboard still works. SSH is useful, but it is not the only route.
Why do permissions still fail after 755 and 644?
The owner or group may be wrong, the server may run PHP as a different user, SELinux may block the write, or the host may require different values such as 750/640 or 775/664.
Should I set WordPress permissions to 777?
No, not as a real fix. 777 makes files or folders writable by everyone. Use it only for a short host-guided diagnostic test, then restore safer values.
Conclusion
WordPress repair permissions usually starts with a simple reset: folders at 755, files at 644, and wp-config.php locked down as tightly as your host allows. That solves many upload, update, and install errors without making the site too open.
If the same error continues, stop changing numbers and look at ownership, hosting rules, storage limits, server security, or user roles. Back up first, use the safest access method you have, and ask your host for the correct owner and group when the evidence points beyond basic permissions.
Shivani enjoys crafting guides that make every aspect of using WordPress simple and easy to follow. When she's not glued to her laptop, you can find her buried in a good book or occasionally, painting.